Four boundaries
Each layer refuses on its own
Operator plane, no content view
Roles checked in the data layer
Your organisation’s boundary
Keys on each device
Layer 1
Who at Enclessa can see your data
A separate control plane that can list, suspend and delete organisations but not read content — enforced by a build check, not a policy.
- Mandatory multi-factor for operators
- No impersonation, no silent support access
- Separate platform audit log
Layer 2
Access control
Permissions are evaluated in the data layer, so an ungranted capability is absent, not hidden. A role never carries a permission its author lacks.
- One transferable owner
- Passkeys and TOTP
- SAML 2.0 or OpenID Connect SSO, SCIM 2.0
- Bot tokens scoped to named operations
Layer 3
Tenant isolation
The organisation is asserted at one choke point, not at each call site. Another organisation's object answers not-found, because forbidden would confirm it exists. 286 API operations are probed across the boundary; all are refused.
- Probe suite generated from the OpenAPI document
- A regression fails the build
- Files and audit records carry their organisation
Layer 4
Encryption
MLS through OpenMLS, compiled once in Rust for every client. Each device is a group member: adding one is visible, removing one re-keys.
- One key per device, never one per account
- The server only delivers
- Encrypted key backup
- TLS in transit, managed content encrypted at rest
In the product
Permissions you can read, an operator plane that cannot read you
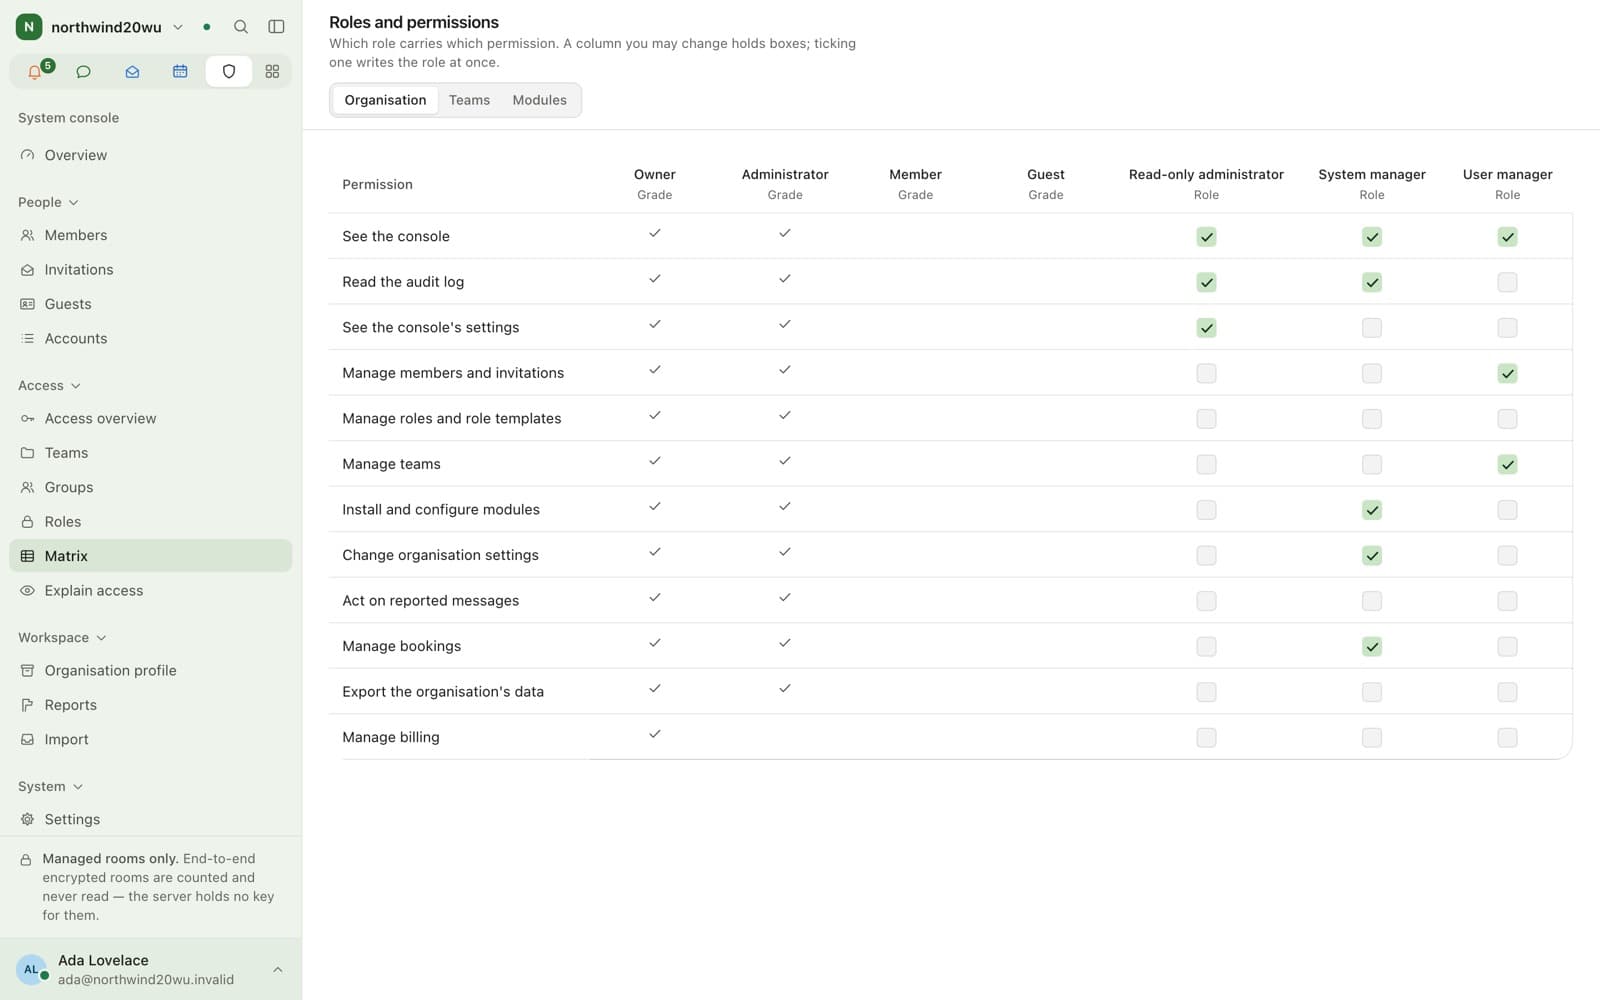
The permission matrix.
Enclessa operators
Metadata only
- List organisations
- Suspend an organisation
- Delete an organisation
- Write every action to the platform audit log
No way in
- Read a channel or direct message
- Open a file or document
- Sign in as one of your people
What Enclessa does not have
Said as plainly as the rest
FAQ
Security questions
- It is built for it: EU hosting, a German seller, a data processing agreement, data-subject export, retention rules and legal holds. The lawful basis stays yours.
- Not encrypted conversations — the server holds no key. The operator plane cannot read managed channels either, and there is no impersonation.
- Yes: everything, any time, in open formats, with a documented data model and API.
- Privately to security@enclessa.app. You get an acknowledgement and a timeline.
Bring your team over this afternoon
Free for up to 10 people, with encrypted direct messages and video calls. No payment card, no time limit, no server to run.
For businesses and organisations only — not available to consumers.